
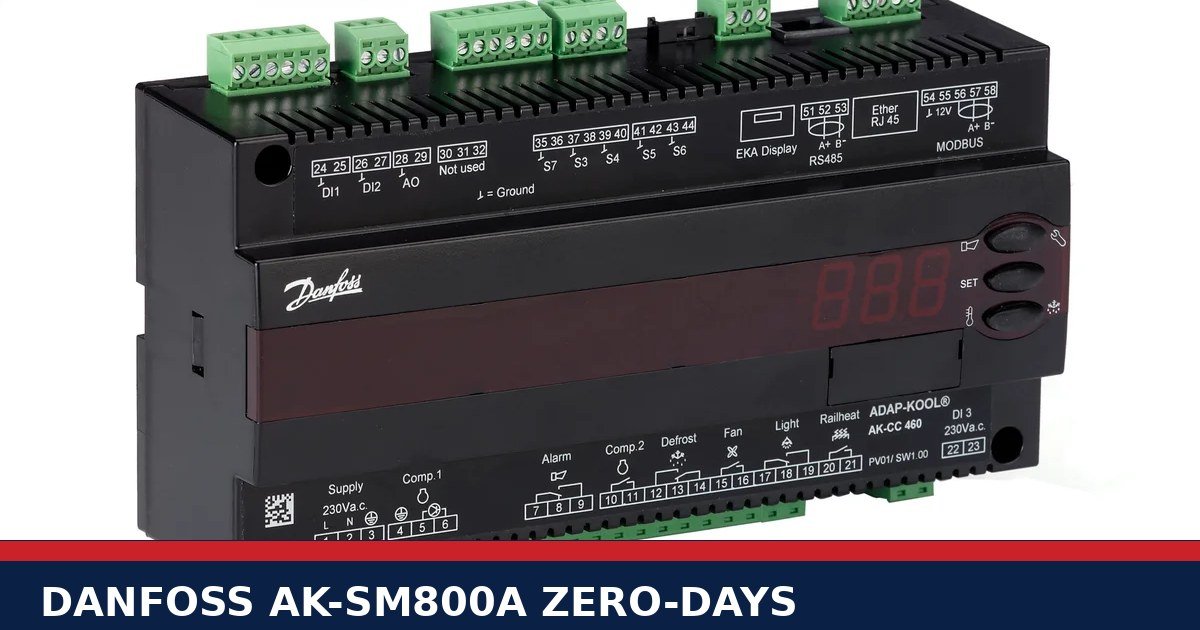
A Dutch security researcher found six new pre-authentication remote code execution flaws in the Danfoss AK-SM800A refrigeration controller in under an hour of manual firmware review, with no AI assistance and no fuzzing. All firmware versions up to and including 5.3.2 are affected. There is no patch, no CVE number has been assigned, and the researchers say the newest firmware, 5.4.0, does not fix them either. The Danfoss AK-SM800A zero-day vulnerabilities land in the middle of an ongoing campaign against internet-exposed refrigeration controllers that has already drawn a joint warning from five US government agencies, and the researcher’s verdict is blunt: patching alone is not enough, and operators should take these controllers off the internet.
How the Danfoss AK-SM800A zero-day vulnerabilities were found in under an hour
Carlo Meijer, a Dutch researcher at Midnight Blue, examined version 5.3.2 of the AK-SM800A firmware, the latest at the time, by hand. He went looking in places where the firmware calls strcpy, a function that does not check whether the destination buffer is large enough. He reported finding five cases where a one-line cURL command could trigger a segmentation fault, according to The Register, which covered the disclosure on 17 November.
All six flaws are stack-based buffer overflows. At least five of them sit in a small segment of code in the sm_app web task, in unauthenticated CGI handlers. A single crafted request to one of those endpoints can crash the web task, and the researchers demonstrated full remote code execution as root in a proof of concept built against firmware 3.3.0, and state the bugs are present in the latest firmware as well.
The vulnerable code makes hundreds of unsafe strcpy calls in externally reachable, unauthenticated handler functions, and the binaries have no stack canaries and no Position Independent Executable protection. The exploited application runs as root, so a successful exploit gives an attacker remote code execution as root on the controller. The AK-SM800A runs Danux, a custom Yocto-based Linux distribution, on an i.MX6 processor, and firmware images are downloadable from Danfoss’s website.
The disclosure was published by Midnight Blue on Wednesday 11 November, according to Germany’s BSI and a 16 November write-up that read the BSI notice. GBHackers reported it on 13 November. No CVE identifiers have been assigned yet. Midnight Blue is in a coordinated vulnerability disclosure process with Danfoss and is withholding technical details, including the exact endpoints, until disclosure is sorted.
Why strict mode does not stop the sixth flaw
The sixth flaw is the one that matters most for operators who followed the official advice. It sits in sm_fcgi_app, the binary that enforces Danfoss’s strict session control mode. Strict has been the default security level since firmware 4.0, and enabling it was one of CERT-FR’s official mitigations after the October attacks. The researchers demonstrated a segmentation fault against the latest firmware with strict mode on. Strict mode stops the other five flaws, by the researchers’ account, but the sixth is in the gate itself.
That is why the researchers titled their write-up “Don’t bother patching”. Their argument is not that patching is useless in general. It is that piecemeal patching, or enabling strict mode, is a poor use of limited security resources against this codebase, because the flaws are in the code itself and a patch for these six does not exist yet. Danfoss’s November update guide documents a 5.4.0 software package with one security change, a stricter password policy, but the researchers say 5.4.0 does not fix these flaws, and Germany’s BSI says it can no longer rule out that 5.4.0 is affected too.
Danfoss has not published an advisory for these six flaws. Its advisories page, read on 16 November, has no entry for them. Its most recent AK-SM800A entries are older, fixed flaws: CVE-2025-41450, an authentication bypass fixed in 4.2, and CVE-2025-41451 and CVE-2025-41452, fixed in 4.3.1. Two more, CVE-2023-25915 and CVE-2023-25914, were documented in 2023. The six new flaws join at least five previously documented flaws on the same controller, and the demo exploit was built against firmware 3.3.0, while the researchers state the same bugs are present in 5.3.2.
No secure boot: what happens after a break-in
The worst part of the disclosure is what happens after an attacker gets in. The controllers do not use the i.MX6 processor’s secure boot features, verified by checking the responsible One-Time Programmable fuse registers. An attacker with root access could plant an implant that survives a factory reset or a firmware update, or wipe flash memory or push malformed firmware to brick the device, forcing physical replacement.
That persistence risk is what could turn a controller flaw into a food safety problem. A controller bricked by wiped flash or malformed firmware can force physical replacement. The researchers’ recommendation is to inventory every exposed controller, including those behind system-integrator 4G modems, and restrict management access to a VPN, a private APN, or tightly scoped IP allowlists.
According to Censys data cited by Midnight Blue, with a screenshot dated 10 November 2026, hundreds of Danfoss systems are still exposed online, plus more than 1,000 Copeland and Dixell fridge controllers, and controllers from similar vendors such as Eliwell remain exposed in the hundreds. Midnight Blue itself notes that a sizeable chunk of those are by now honeypots, so the figures are an upper bound on exposed real controllers, not a count of vulnerable production units.
Three countries warned in two days
The Danfoss AK-SM800A zero-day vulnerabilities drew warnings from three national agencies on 12 and 13 November. Belgium’s Centre for Cybersecurity published its warning on 12 November, urging operators to remove the controllers’ direct internet exposure immediately. Ireland’s National Cyber Security Centre and Germany’s BSI each published one on Friday 13 November. The Irish advisory says CVE identifiers have not been assigned, no patches are available, and coordinated disclosure with the vendor is ongoing.
The BSI rates the issue 3 on its 4-step scale, orange, act without delay, lists no fixed version, and says it has no information that these six flaws are being exploited. CISA’s Known Exploited Vulnerabilities catalog has no Danfoss entry at all, and these six flaws have no CVE numbers that could be listed. The Register said it asked Danfoss to respond to the findings, but the company did not reply, and that Danfoss has consistently not answered its requests for information since being implicated in the supermarket attacks.
Danfoss’s earlier position was that most affected units in the French attacks were legacy models or ran outdated firmware. That position refers to the attack waves, not to this disclosure, and it does not hold for these flaws: the researchers say they are present in 5.3.2, the latest version at the time of their research, and that 5.4.0 does not fix them. Multiple Danfoss business units hold IEC 62443-4-1 certification for secure product development, which Danfoss advertises prominently, yet the code lacks basic exploit mitigations. That contrast is Midnight Blue’s point, not ours.
The campaign this disclosure lands in
The six flaws are new, but the campaign they land in began in October, one month before the disclosure. Attacks on internet-exposed Danfoss and Copeland controllers began in France on 11 October 2026 and continued in a second wave on 2 November. Attackers triggered defrost cycles, spoiled food, and in some cases started fires, according to GBHackers. The damage has been described as tens of millions of euros of food spoiled, but that figure traces to a single supermarket owner’s estimate, not an official total, so the article presents it as a reported estimate only.
The dated sequence runs like this. On 28 August, a blog first reported rogue freezer behaviour at US military bases, and freezer malfunctions hit roughly six US military commissaries in late August. On 11 October came the first attack wave in France, hitting more than 350 establishments according to Reuters. France’s CERT-FR issued its alert on 12 October. On 29 October, Reuters reported the Pentagon was treating the US incidents as a suspected cyberattack. On 1 and 2 November, a French blood bank attack hit three sites and was caught in time with no blood lost, and a second supermarket wave spread across Europe. On 4 November came a European joint warning, and on 5 November a US joint warning from CISA, the FBI, HHS, USDA and the Department of Transportation. Midnight Blue published its disclosure on 11 November, six days after the US warning.
Two things must not be conflated. No source claims these six new flaws were used in the October and November attack waves, which predate this disclosure, and no entry point for those waves has been confirmed. And the previously known flaws on this platform, the authentication bypass CVE-2025-41450, OS command injection CVE-2023-25915, and path traversal CVE-2023-25914, are separate from the six new ones. CVE-2025-41451 and CVE-2025-41452 were also fixed in 4.3.1. Public proof-of-concept exploits for those appeared within 48 hours of the French attacks. Separately, 23 vulnerabilities were recently disclosed in Copeland XWEB Pro controllers that could give attackers root access.
What should I do if I run an AK-SM800A?
If you run a Danfoss AK-SM800A, take it off the internet now. No patch exists for these six flaws, and strict mode does not stop all of them. Put management access behind a VPN, a private APN or a tight IP allowlist, and inventory every exposed controller, including those behind 4G modems.
- Remove the controller’s direct internet exposure today, and do not wait for a patch to arrive.
- Inventory every exposed controller in your estate, including units reachable through system-integrator 4G modems.
- Put management access behind a VPN, a private APN or a tightly scoped IP allowlist.
- Check whether firmware 5.4.0 is installed, and do not assume it fixes these flaws.
- Watch Danfoss’s advisories page and the BSI notice for CVE numbers and a patched firmware.
These steps follow the researchers’ own advice and the BSI notice, not a Danfoss instruction. Danfoss has not published an advisory for these flaws. Danfoss’s own standing advice, from its advisories page, is that the AK-SM800A must not be directly reachable from the internet, on any version.
What to watch next
Three things are worth watching in the Danfoss AK-SM800A zero-day vulnerabilities story. First, CVE assignment: the six flaws have no identifiers yet, and a CVE number would give operators an identifier to track and a fix to watch for. Second, Danfoss’s response: the company did not reply to The Register’s request for comment and has published no advisory for these flaws, so any statement or patch is worth watching. Third, the full technical disclosure once coordinated disclosure with Danfoss concludes, and any further developments in the campaign. Until then, the facts are six flaws, found in under an hour in firmware 5.3.2, which the researchers say are not fixed in 5.4.0, with no patch, no CVE, no advisory from Danfoss, and no reply to The Register’s request for comment.


